Maersk cyber attack 2026: why an acquired system fell
APJ-RAISE team · · 7 min read
The 2026 Maersk cyber attack was a data theft from one old, local system that Maersk got when it bought another company. Maersk disclosed it on 11 November 2026 and says shipping is running normally.
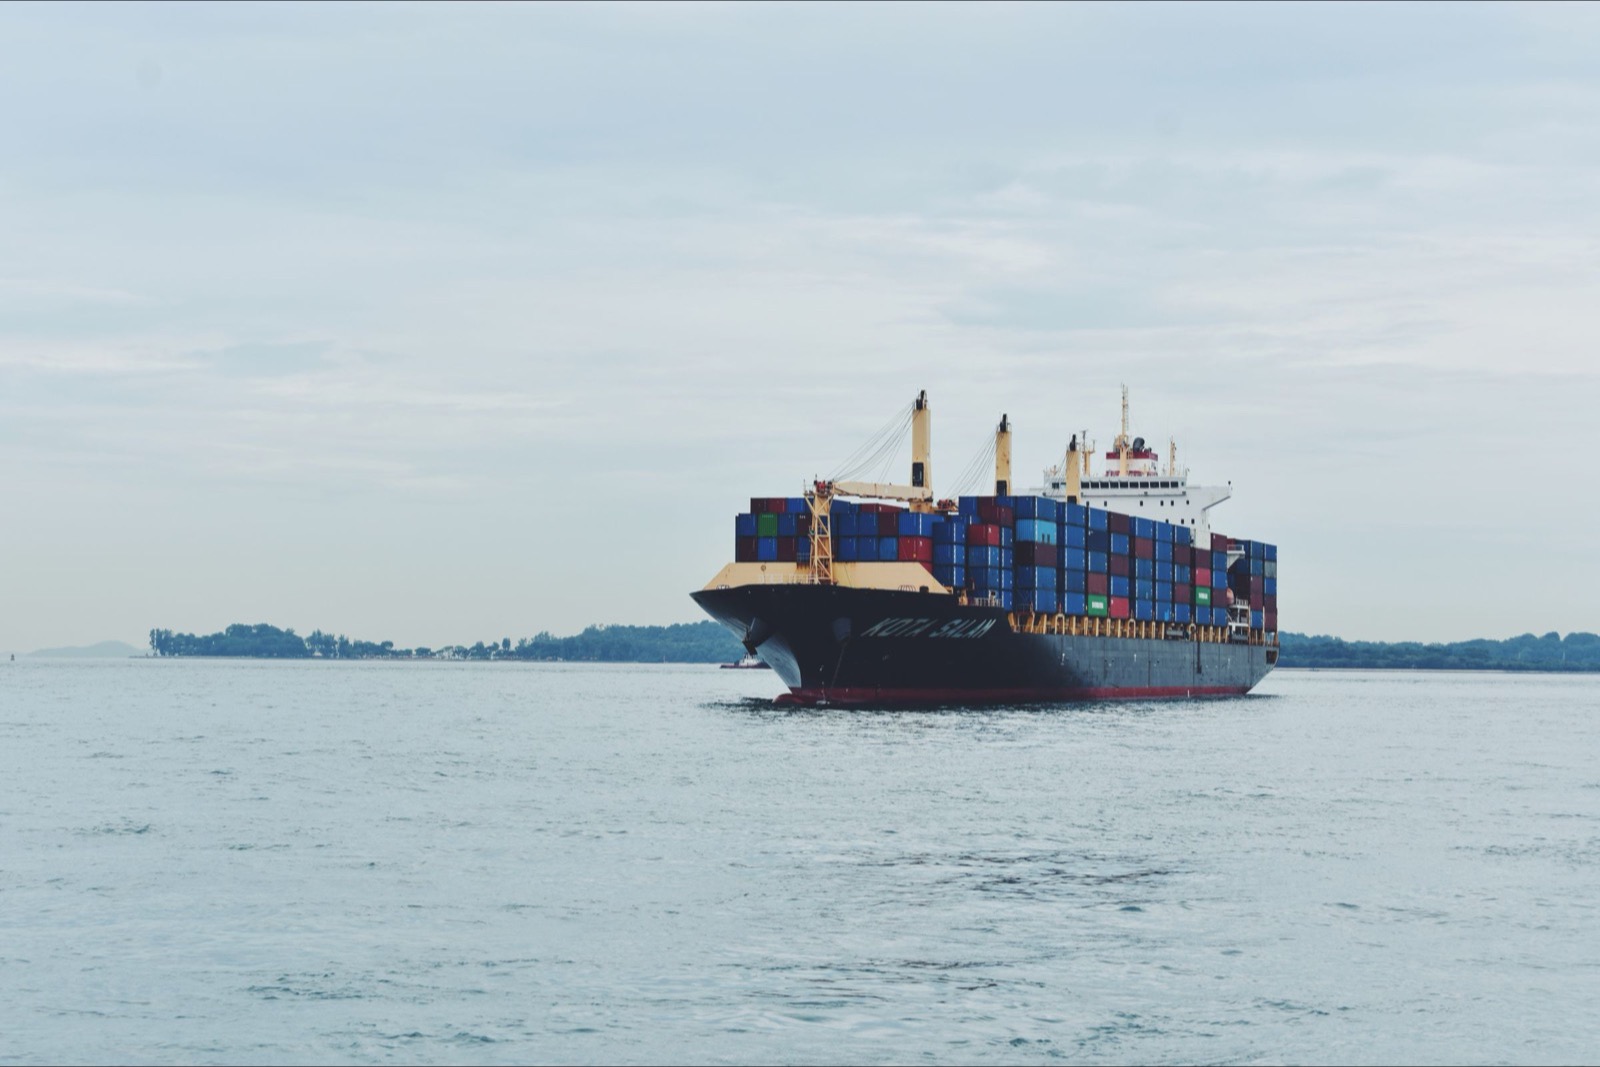
That one detail, a system "from a previous acquisition", is the real story. Big companies rarely get breached through their main platform. They get breached through the corner nobody fully owns. This post uses Maersk to ask a simple question: why do systems that come with an acquisition get breached so often? Facts are as of 18 November 2026.
Maersk cyber attack 2026: what happened
Maersk says attackers got in and copied data from one of its local legacy systems. Its security team opened an investigation and secured the system. In its advisory, Maersk said its findings so far "strongly suggest no sensitive data has been disclosed".
Maersk also said the incident is limited to that local system. It saw no sign of impact on its other systems, or on the customer and partner systems that link to it through APIs and EDI. EDI (electronic data interchange) is how firms swap shipping orders and invoices by machine. Customers can book and manage shipments as usual. Maersk warned people to be careful with any unexpected messages that claim to be about the incident, since scammers like to follow a breach.
The advisory leaves a lot out. It does not name the system, the acquired company, the attacker, the way in or the date.
What WhiteArmor claims, and what is confirmed
A ransomware and extortion group called WhiteArmor claimed the attack about three days before Maersk spoke, according to The Record. Every point in this list is a claim by the attackers, repeated by news sites. Maersk has confirmed none of it.
- Size: about 100 GB of data.
- Source: LF Logistics, a Hong Kong firm Maersk bought (The Record).
- Contents: nearly 30,000 driver records, plaintext passwords, admin account details, delivery receipts and phone logs (teiss).
- Demand: US$5 million in Bitcoin within 30 days, or the data goes public.
Maersk finished buying LF Logistics from Li & Fung in August 2022. So the link to LF Logistics fits the word "acquisition", but it is still a report, not a Maersk statement.
One tension is worth watching. "Data extraction" and "no sensitive data" can both be true if the stolen files were mostly routine business records. They cannot both be true if the plaintext password claim holds. Only Maersk's final findings, or a leak, will settle that.
Why do systems from acquisitions get breached?
An acquired system gets breached because it holds real data but sits outside the buyer's normal security. Security teams call this M&A tech debt (M&A means mergers and acquisitions). What follows is the general pattern seen across the industry. It is not a finding about Maersk's actual system, which Maersk has not described.
Start with time. Using Maersk's own dates, August 2022 to November 2026 is about 51 months. That is our own count, and it assumes the reported LF Logistics link is right. Four years sounds long enough to merge one system. In practice it often is not, for plain reasons:
- The data still matters. Driver records, contracts and delivery history keep an old system switched on long after the deal.
- The people left. Staff who knew how the system worked often move on after a takeover.
- Login rules stay old. A system built before the deal may still accept a password alone, with no MFA.
- Monitoring lags. The buyer's alerts and logging may never have been wired into it.
- Patches slip. Old software can drift past its support date while everyone waits for the migration.
Attackers do not need to know any of this in advance. They scan for whatever answers, and an old, half-forgotten server answers. The same idea, entry through a trusted side door rather than the main product, drove the Storm-0940 Microsoft 365 breach this autumn.
A quick check for any acquired system
If you work in IT, or you are writing a case study, these five questions expose most M&A tech debt. Each one has a yes or no answer, so you can score a system in a few minutes:
- 1Is the system in the buyer's asset list, with a named owner today?
- 2Does every login to it require MFA, including admin and service accounts?
- 3Do its logs reach the buyer's security monitoring, and has anyone looked at them this month?
- 4Is its software still inside vendor support?
- 5Is there a written date to migrate or switch it off?
Every "no" is a door. The WhiteArmor claim about plaintext passwords, if true, would be a failed answer to question 2 and probably question 3 as well.
Maersk cyber attack 2017: NotPetya in short
Many readers mix up 2026 with the far bigger NotPetya attack of 27 June 2017. NotPetya looked like ransomware, but paying could not undo it. It wiped machines. Andy Greenberg's 2018 WIRED story is the main source here.
Russian military hackers had hijacked the update servers of M.E.Doc, a Ukrainian tax program, and used them to push the malware. Maersk was exposed because one finance executive in its Odessa office had asked for M.E.Doc on a single computer. Inside the network it spread with EternalBlue, a leaked NSA exploit for unpatched Windows, and Mimikatz, a tool that pulls passwords from memory.
Maersk chair Jim Hagemann Snabe gave the damage figures at the World Economic Forum in January 2018. The company rebuilt 4,000 servers, 45,000 PCs and 2,500 applications. The core network took about 10 days, and full recovery close to two months. The cost was US$250 million to US$300 million. Snabe said shipping volume fell by only about 20 percent, thanks to manual work.
Our own sum from those numbers: 4,000 servers plus 45,000 PCs is 49,000 machines. Dividing US$250 to 300 million by 49,000 gives roughly US$5,100 to US$6,100 per machine. That is a rough figure, since the cost also covered lost business, but it shows how expensive a wipe gets.
Recovery hinged on luck. Maersk had about 150 domain controllers, the servers that hold every user and password on a Windows network. They copied to each other, so the plan treated each as a backup of the rest. NotPetya wiped them all at once. A single one in Ghana survived because a power cut had taken it offline. The link was too slow to copy its data, so a staff member flew the drive to Nigeria, where a colleague carried it on to London. WIRED also reports that some servers still ran Windows 2000, and that a security upgrade approved in 2016 had not been done.
Maersk 2017 vs 2026: the difference
- Type: 2017 was a wiper. 2026 is data theft with an extortion claim.
- Scope: 2017 hit the whole company. In 2026 Maersk says one local system.
- Shipping: 2017 stopped ports and bookings. In 2026 Maersk reports no disruption.
- Attacker: 2017 is blamed on Russia's military. 2026 is claimed by WhiteArmor, unconfirmed.
- Money: 2017 cost up to US$300 million. The 2026 ransom claim is US$5 million.
Put the last line in proportion. The claimed ransom is about 2 percent of the low NotPetya cost estimate (5 ÷ 250), by our sum. Yet the two cases share a root cause. In 2017 one PC with one niche tax program was the way in. In 2026 it was, by Maersk's own words, one local system from a deal. In both, the smallest, least watched part of the company set the risk for all of it.
What most coverage of the Maersk breach gets wrong
Some headlines treat the 100 GB and the 30,000 driver records as facts. They are the attackers' own numbers, and extortion groups have every reason to inflate them. Other stories reuse NotPetya photos and figures, which makes 2026 sound like a second global shutdown. It is not, on current evidence. Also note that "no sensitive data" is Maersk's early finding, not a final one, so it can still change.
For more on attacks against Indian firms, read our post on CERT-In's CRAFTY FALCON advisory. Many 2026 intrusions start with weak credentials, which is why AI agent identity is now a security topic. To judge sources like these, try our course on reading and reviewing papers.
Questions people ask
- What happened in the Maersk cyber attack 2026?
- On 11 November 2026, Maersk said attackers accessed and copied data from one old local system from a previous acquisition. Maersk says it has seen no sign that sensitive data was disclosed and no disruption to shipping.
- Is the 2026 Maersk breach linked to LF Logistics?
- News reports link it to LF Logistics, which Maersk bought in 2022. Maersk has only said "a previous acquisition" and has not named the company.
- How much did the Maersk cyber attack 2017 cost?
- Maersk chair Jim Hagemann Snabe estimated US$250 million to US$300 million. Maersk rebuilt 4,000 servers, 45,000 PCs and 2,500 applications after NotPetya hit on 27 June 2017.
- What was the Maersk cyber attack in Ghana?
- There was no attack in Ghana. During NotPetya in 2017, one Maersk domain controller in Ghana survived because a power cut had taken it offline, and its copy helped rebuild the network.
Sources
- 1.A.P. Moller - Maersk. IT security incident. Maersk advisory, 11 November 2026.
- 2.Jonathan Greig. Shipping giant Maersk says recent cyber incident affected legacy system. The Record, 12 November 2026.
- 3.Rob O'Dwyer. Maersk investigates data breach involving legacy IT system. Smart Maritime Network, 12 November 2026.
- 4.WhiteArmor claims Maersk network breach, demands $5 million ransom. teiss, 16 November 2026.
- 5.A.P. Moller - Maersk. A.P. Moller - Maersk completes acquisition of LF Logistics. 31 August 2022.
- 6.Andy Greenberg. The Untold Story of NotPetya, the Most Devastating Cyberattack in History. WIRED, 21 August 2018.
- 7.Pierluigi Paganini. Maersk chair revealed its company reinstalled 45,000 PCs and 4,000 Servers after NotPetya Attack. Security Affairs, 25 January 2018.